Authorize
AP2 mandates · x402
AP2 v0.2 open/closed Checkout and Payment Mandate correlation before wallet execution (legacy v0.1 intent/cart ids accepted). Compatible with AP2 (FIDO Alliance) and x402 Foundation patterns.
Independent verification · No login
Intercept tools and gateways log what happened inside their platform. Aevesa produces portable proof (permit or deny) that auditors verify at verify.aevesa.com without logging into your gateway, intercept vendor, or Aevesa admin console.
For agentic finance: block explorers show what landed on chain. Aevesa binds intent, policy, and conduct to the transaction (Base, Solana, Tempo; AP2, x402). Hash-only proofs with optional anchor digests. Not a chain protocol, not custody, no token.
Post-tx proof card · Launch checklist (Solana) · Request enterprise briefing · Dashboard login
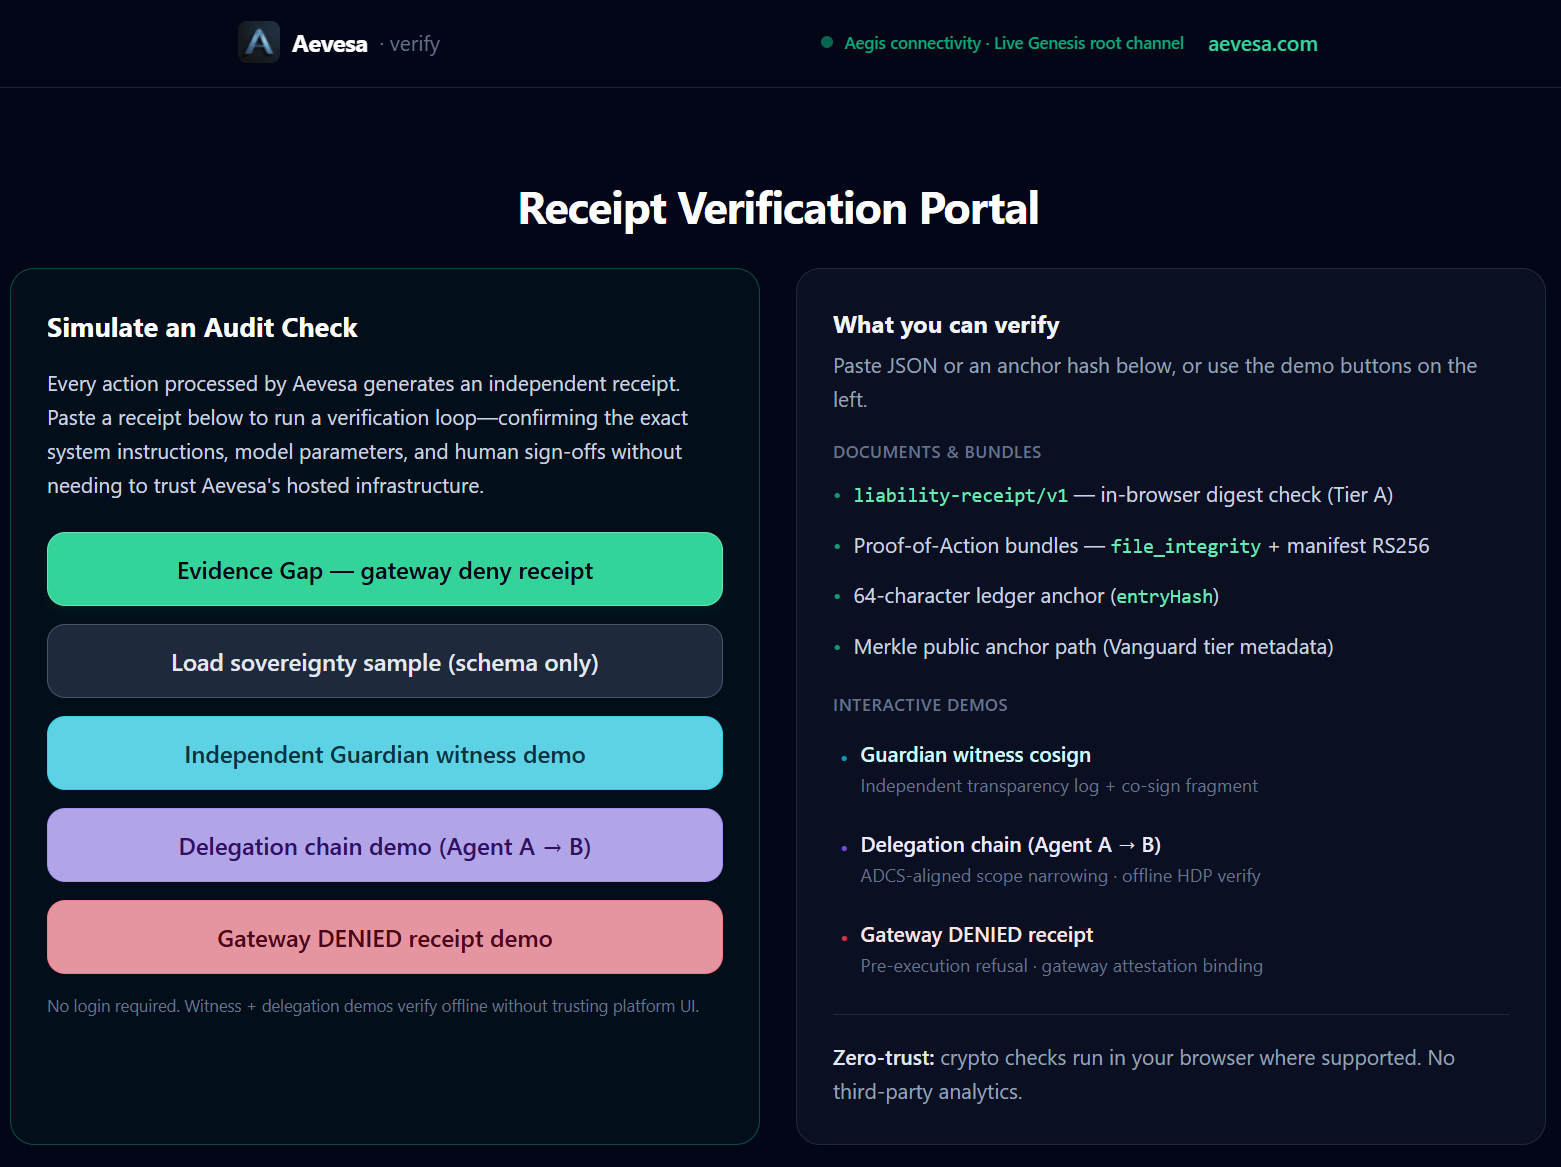
VERIFIED or TAMPERED runs here without leaving this page.Security / GRC
Can my auditor verify without our vendor?
Run the portability drill: verify a receipt with no gateway login or API key.
Portability drill demo →
Platform engineering
Where does Aevesa sit in the stack?
Route → intercept → classify → prove → verify. Complement gateways and AI-SPM; do not replace them.
Reference architecture →
Diligence / MGA
Set complete ≠ uniformly enforced
See chain enforcement rollup and weakest-link disclosure on a multi-hop session export.
Mixed-enforcement demo →
Agentic finance / wallets
Who proves the agent before the tx lands?
Wallet ingest, AP2/x402 conduct, and on-chain action packs with optional Base, Solana, or Tempo anchor bundles. Verify offline.
On-chain conduct demo →
The Evidence Gap
Intercept tools and AI-SPM platforms govern what agents can touch. Aevesa proves what happened.
Intercept vendors decide allow/block. Aevesa proves the decision happened, verifiable offline without their admin login.
Intercept and classify layers leave a gap in the architecture diagram: no portable proof an external auditor can verify offline. Regulated teams cannot sign off on agent deployments using vendor-scoped JSON alone. Paste a receipt at verify.aevesa.com and recompute integrity in under 90 seconds. No login required. Aevesa cosigns material decisions to an independent witness log, not another platform dashboard. Production tenants run Assurance Autopilot, nightly cryptographic drift checks with an Assured / Drift badge your CISO can review.
82%
Executives confident policies protect agent actions (Gravitee 2026)
~14%
Deploy agents with full security / IT approval
90s
Offline verify at verify.aevesa.com: the Prove Gap in action
Read The Prove Gap Report v1.0 · PMM self-assessment · Research sources
All demos on verify.aevesa.com Explore no login · independent verification
Reference architecture
Complement · not replacement
Already routing through a gateway, intercepting add-ons, and classifying with AI-SPM? Aevesa is the Prove layer your architecture diagram is missing.
Agent wallets on Base, Solana, and Tempo, x402 and AP2 mandate correlation, AgentKit-shaped ingest get the same Prove layer as enterprise gateways. Wallet policy engines enforce before money moves and keep their own audit trail; Aevesa adds the part none of them publish: a receipt a third party recomputes offline without trusting the wallet, the agent, or Aevesa.
How it fits the standards: Verifiable Intent (Mastercard + Google, FIDO Alliance) proves what the user authorized. ERC-8004 publishes who vouches for the agent. Aevesa proves what the agent actually did, bound to the tx hash and the policy that governed it.
Your gateway routes. Intercept tools vet and block. AI-SPM classifies. Aevesa notarizes and proves what happened.
Most platform diagrams stop before Prove. Aevesa cosigns permit/deny and intercept decisions into entryHash + liability-receipt/v1 artifacts anyone verifies offline. Agentic finance layers first, then an example enterprise stack (Unity AI Gateway + AIR Security + Cyera + Aevesa). Also works alongside Portkey, Noma, Zenity, Obsidian, and your existing GRC tools.
Agentic finance stack
Authorize
AP2 v0.2 open/closed Checkout and Payment Mandate correlation before wallet execution (legacy v0.1 intent/cart ids accepted). Compatible with AP2 (FIDO Alliance) and x402 Foundation patterns.
Execute
Wallet events and on-chain action attestations bound to policy digests. Optional chain anchors; Rekor/SCITT witnesses when configured.
Prove
on-chain-action-attestation/v1, AP2 conduct receipts, chain-anchor export bundles. Offline verify at verify.aevesa.com.
What we do not prove: chain inclusion unless a chain anchor is attached and disclosed; that the user’s intent was correct; custody or settlement finality. Receipts prove integrity relative to the disclosed capture path.
Example enterprise AI-SPM stack
Route
MCP routing, service policies, wire-level guardrails inside Databricks.
Intercept
Vet add-ons, block tool calls, MCP posture. Decisions live in vendor dashboards until Aevesa notarizes them.
Classify
Data-centric runtime protection, classification tags, AI-SPM inventory.
Prove
Intercept attest & ledger anchor: portable receipts bound to decision_digest. Witness cosign to independent transparency log. On-chain action attestation binds policy and conduct digests to tx hash; optional chain anchor disclosure (Base, Solana, Tempo).
Verify
verify.aevesa.com · @aevesa/verify. No vendor login.
| Layer | Owner | Output |
|---|---|---|
| RouteRoute + guardrail | Unity AI Gateway | Service policies, MCP routing |
| InterceptVet + block | AIR Security, Noma, Zenity | Allow/deny/quarantine decisions (vendor-scoped until notarized) |
| ClassifyClassify + protect | Cyera AI Guardian | Runtime block, data classification tags |
| ProveAttest + anchor | Aevesa | entryHash + liability-receipt/v1 on-chain-action-attestation/v1 · chain-anchor-export-bundle (when anchored) |
| VerifyIndependent audit | Auditor (no login) | verify.aevesa.com · @aevesa/verify |
Land with intercept attest only (one webhook after permit/deny). Complements AIR Security, Unity AI Gateway, Cyera AI Guardian, Noma, Portkey, and observability or GRC sinks you already run. Expand to MCP receipt-before-action when agents run outside a managed gateway path.
Third-party trademarks.
Coinbase, Base, Solana, Coinbase AgentKit, x402 and the x402 Foundation (Linux Foundation), AP2 (Agent Payments Protocol, FIDO Alliance; originated by Google), Verifiable Intent (Mastercard, Google), ERC-8004, Mastercard, Visa, Stripe, Tempo, and related marks are trademarks of their respective owners.
Databricks, Unity AI Gateway, Cyera, Cyera AI Guardian, AIR Security, Noma Security, Zenity, Obsidian Security, Portkey, and related marks are trademarks of their respective owners.
Diagrams and integration examples describe complementary patterns only; Aevesa is not affiliated with, endorsed by, or sponsored by those vendors or standards bodies unless we state otherwise in a signed agreement.
aegis/1 is Aevesa’s ledger preimage spec and is unrelated to Project Aegis or any other product named Aegis.
Differentiation
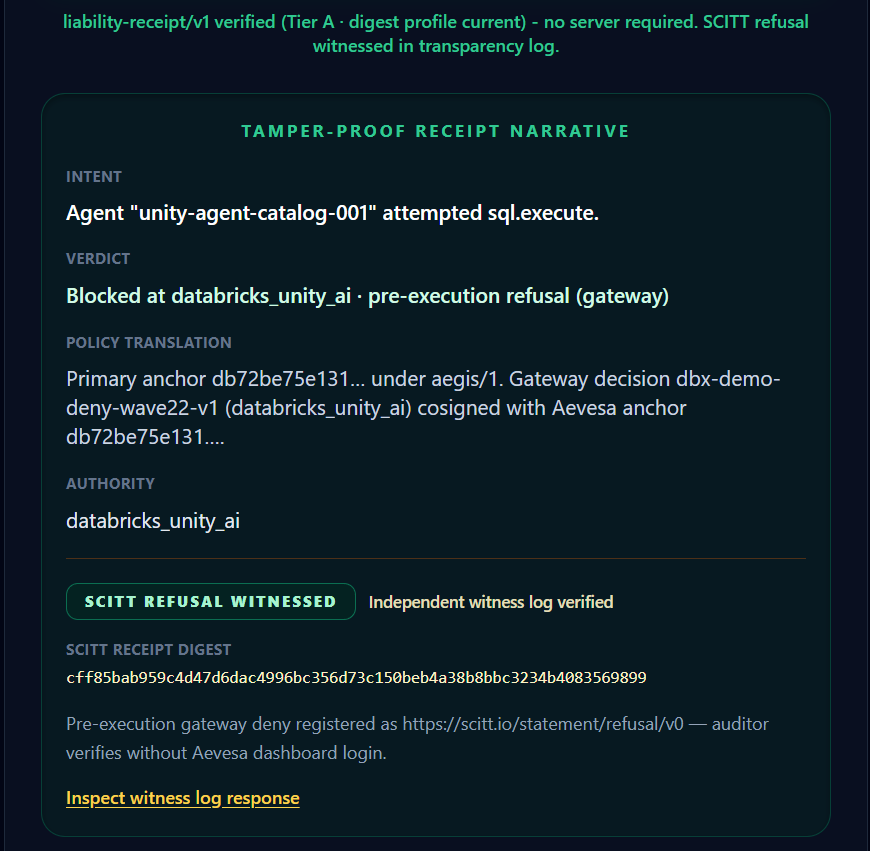
Gateways route traffic; intercept tools vet and block. Aevesa adds the Prove layer, cosigning permit/deny decisions into tamper-proof receipts you verify offline without trusting any vendor UI.
{
  "lvl": "INFO",
  "_trace": "chunked…",
  "ts": "2026-05-13T18:42:01.883Z",
  "svc": "ai-gateway",
  "rid": "req_9f2c4a",
  "route": "/v1/chat/completions",
  "body": "{\"messages\":[…]}",
  "model": "gpt-4o",
  "latency_ms": 842,
  "policy_ref": null,
  "signed_decision": null,
  "flush": "pending_batch_7"
}
{
  "schema": "liability-receipt/v1",
  "receipt_id": "sr_01k8q2x7hmz",
  "decision": "DENY",
  "gateway_decision_id": "dbx-demo-deny-001",
  "gateway_event_hash": "f302e2de8ab0ec26bbf0f4d6e9d87d36ca05273867219e114677005c7b7de826",
  "entry_hash": "26988e6613b9dedfb9145e454ad215556862338d674bc0fa7d5a7660867e0666",
  "integrity": {
    "receipt_digest": "0346fb5f41e45d81715ed55eb36c2c00578397dc739c8111890d7a8b62041010",
    "signature_alg": "Ed25519"
  },
  "verify": "https://verify.aevesa.com?demo=gateway"
}
Side-by-side gateway log vs portable receipt (hashes match the live gateway attest demo). The full feature comparison lives on The Prove Gap.
Deploy gateways for how traffic flows. Deploy Aevesa for what was permitted. You get proofs your auditors can recompute.
Trust center
Public specs and diligence packs with no login, no NDA gate for the technical baseline. Request a briefing when you need deployment topology and fail-mode walkthroughs.
Fail-mode matrix, EU AI Act prEN mapping, OWASP ASI controls, MCPShield coverage, threat model, and published SLOs.
Open trust bundle →liability-receipt schema, offline @aevesa/verify, and the Open Evidence API your auditors can call independently of our UI.
Gateway attest → liability receipt → offline verify in under five minutes. Reference flows for standards and procurement reviewers.
Browse conformance lab →Need deployment topology or a fail-closed walkthrough? Request a technical briefing · Protocol repo
Aevesa routes every agent intent through two enforcement paths. Routine actions clear in milliseconds. High-stakes actions pause for a human decision, and that decision becomes a tamper-proof activity receipt.
Tamper-Proof Receipt
Every high-risk intervention generates a tamper-proof activity receipt. This isn't just a log entry; it's a cryptographically signed artifact your auditors can recompute offline (distinct from a wallet transaction signature).
dh_sha256:a3f9e1c2b804d57f3a91e6c4d2b30e7a1f58c9d6e2a04b73f1c8d5e9a2b30c74
Before/after deployment benchmarks for security and audit teams: Enterprise deployment comparison.
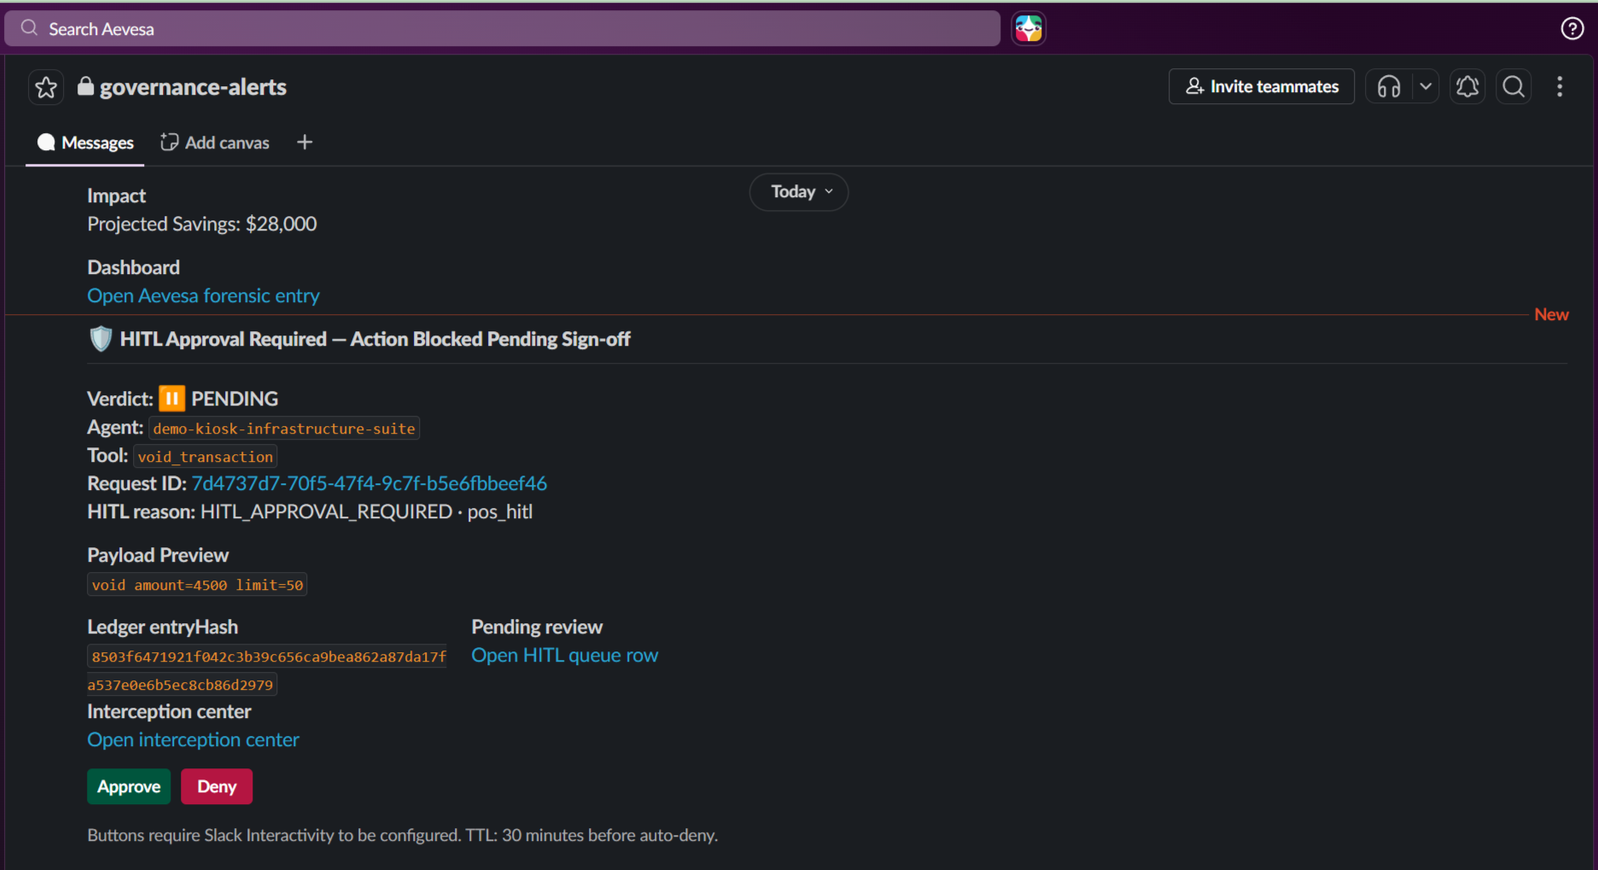
When Aevesa intercepts a high-stakes action, your team gets an instant Slack alert with agent, tool, payload preview, and ledger entryHash. Approve or deny in one click. The decision is hash-chained with a forensic link your auditors can follow offline.
Slack said yes. Aevesa proves yes to what: the HITL approval receipt cryptographically binds approver identity to the exact tool-call digest (hitl-approval-receipt/v1, ASI09-shaped). Try the HITL approval demo.
Go deeper
The homepage stays focused on verify-first proof. Technical comparisons, APoR protocol detail, and product screenshots live on dedicated pages.
Full vendor-log vs portable-receipt comparison tables and the 90-second Evidence Gap demo path.
Prove Gap comparison →
Without vs with Aevesa: audit evidence, gateway deny proof, HITL sealing, and incident cost context for enterprise buyers.
Enterprise benchmarks →
Protocol layer detail, evidence-grade gauntlet, architecture diagrams, and the sovereign evidence vault tour.
Why Aevesa →
Aevesa
Six evidence tiers (Sandbox through Fortress). Start with a verifiable receipt at verify.aevesa.com; scale to Art. 12/14 export packs and Assurance Autopilot. Contact sales for pricing and procurement.
Aevesa
Self-serve governance POC: ship a verifiable receipt to your security buyer
Free to start
Aevesa
Land with gateway attest: one webhook after permit/deny, verifiable receipts from day one
liability-receipt/v1 mint + verify.aevesa.comAevesa
Professional teams: hash-chained integrity on every tier; Vanguard adds Merkle-tree audit layouts and advanced hardening
Aevesa
For compliance-driven organizations standardizing governance, evidence, and identity controls
Aevesa
Enterprise governance with deployment control, custom policy, and white-glove audit execution
Aevesa
Custom deployment for global enterprises: private instance, BYOK, and hands-on audit engineering
Usage-based anchors
Verification on verify.aevesa.com stays free for auditors and third parties. Production ledger writes consume metered anchor credits (SaaS billing, not a protocol token). Self-serve packs: 10 for $10, 50 for $40, 200 for $120 via Stripe, Base USDC, or Solana USDC.
New accounts include starter credits. Paid tiers also bundle anchor credits. Optional on-chain anchor submits are env-gated and disclosed in proof-strength exports.
Buy anchor credit packsSHA-256 Hash Chained
AES-256 Encrypted
Runtime interception, tamper-proof activity receipts, and how Aevesa differs from gateway-only stacks or plain audit logs.
Open full FAQCompliance exports, retention, integrations, and deployment patterns.
Start with the 90-second Evidence Gap demo, then reach out when you want a briefing.
Contact Sales opens a pre-filled email to sales@aevesa.com (no copy and paste required). Agentic finance design partners: use the preset below.
Prefer web mail? Open in Gmail or Outlook web
Compliance-ready infrastructure for Global Standards
Audit-ready infrastructure with hash-chained evidence, access controls, and a published trust bundle. SOC 2 Type II attestation in progress where applicable.
Edge-first enforcement with local verification paths. GDPR-aligned data handling and zero customer source code storage.
Enterprise-grade encryption (AES-256) with hash-chained audit trails and access control federation. BAA and deployment hardening available on enterprise tiers.